Audit and RPO target
We map every data source on your site, files, uploads, database tables, custom storage, and set realistic RPO and RTO targets with you. Commerce, membership and high traffic sites get tighter windows than a brochure site.
Built for UK SMEs, charities, professional services firms and distributed teams around London, Manchester, Birmingham, Bristol, Edinburgh and teams working nationwide. Tested recovery procedures with backups that are useful when an incident actually happens. We account for plain UK English with accessible, task-focused content, cards, Direct Debit and regulated Open Banking or Pay by Bank providers where they fit the journey, and practical delivery in GMT/BST.
UK organisations do not need a generic overseas template. They need WordPress backup and disaster recovery shaped around a competitive market where credibility, accessibility and a low-friction enquiry or checkout journey strongly affect conversion, internal ownership and the tools their customers already recognise. Retention, encryption, storage location, recovery-point objectives and recovery-time objectives are agreed instead of assuming one backup schedule suits every site.
We treat backup and disaster recovery as one practice. Off-site copies on independent infrastructure, hashed for integrity, restored into a throwaway sandbox on a schedule. Real RTO and RPO numbers, a written incident runbook, on-call procedure when minutes matter. If it has not been restored, it is not a backup.
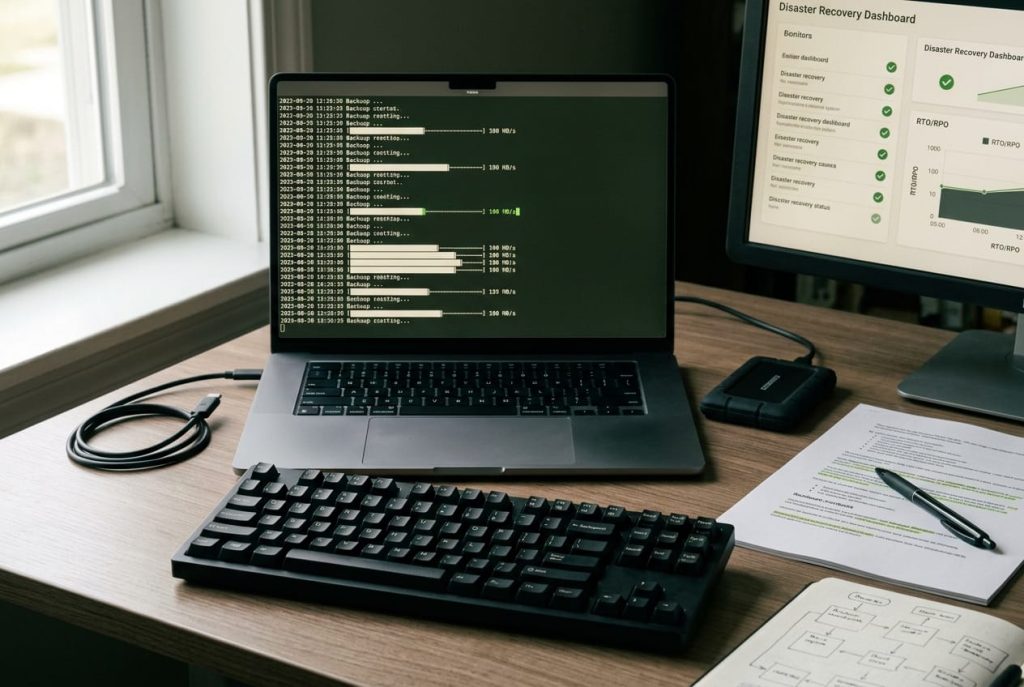
A practical delivery process for UK teams, with decisions documented in GMT/BST and local operational requirements agreed before build work begins.
We map every data source on your site, files, uploads, database tables, custom storage, and set realistic RPO and RTO targets with you. Commerce, membership and high traffic sites get tighter windows than a brochure site.
We provision S3 or Backblaze B2 with least-privilege IAM, lifecycle rules, versioning and immutable retention. Encryption in transit and at rest, keys held by you, geo separated from the production host.
Daily, hourly or streaming database backups depending on tier. Pre and post hooks for plugin updates, checksum verification on upload and alerts when a job fails or takes longer than expected.
A monthly restore into a sandbox environment, validated with a smoke test. You get a written report, a dated runbook and a named on-call contact so recovery is not improvised when you actually need it.
UK SMEs, charities, professional services firms and distributed teams operate in a competitive market where credibility, accessibility and a low-friction enquiry or checkout journey strongly affect conversion. We shape the WordPress backup and disaster recovery around those buying habits, plain UK English with accessible, task-focused content, straightforward proposals, sensible estimates and pricing in pounds, and the systems already used by the team. The result is a practical service plan for teams building trust and sustainable growth across the UK.
Protect orders, customer records and catalogue changes with a recovery plan that accounts for data created between backups. For teams around London, Manchester, Birmingham, Bristol, Edinburgh and teams working nationwide, we define the local audience, ownership and follow-up route before implementation and account for cards, Direct Debit and regulated Open Banking or Pay by Bank providers where they fit the journey.
Restore forms, portals or publishing workflows quickly enough for staff to continue serving customers.
Keep encrypted, off-site copies and a documented restoration sequence for cyber incidents or supplier failure.
We minimise unnecessary collection and document forms, analytics, processors and retention choices with the UK GDPR and Data Protection Act 2018, with security and privacy-by-design guidance from the ICO in mind. Technical implementation supports your compliance work; it does not replace legal advice.
The delivery plan can account for cards, Direct Debit and regulated Open Banking or Pay by Bank providers where they fit the journey, pricing in pounds sterling, plain UK English with accessible, task-focused content, and a UK region when contracts, latency or organisational policy make local hosting preferable. We only add local integrations that serve a real customer or operational need.
Planning, reviews and support are organised around GMT/BST. Retention, encryption, storage location, recovery-point objectives and recovery-time objectives are agreed instead of assuming one backup schedule suits every site. Handover is written for the people who will publish, approve and support the site locally.
Local regulatory references are implementation context, not legal or regulatory advice. Your organisation remains responsible for confirming the obligations that apply to its sector and use of personal data.
A plugin backup is not a DR plan. A host snapshot is not off-site. Here is how we stack up on work that actually brings a site back when it matters.
Pricing reflects site size, commerce scope and recovery target, not hours burnt. Pick a tier close to your needs or ask for a custom estimate after the audit.
Single WordPress site, daily off-site backups, quarterly restore drill. For blogs and brochure sites that simply need a safety net.
WooCommerce or membership site, hourly database and daily full, monthly restore drill. Order and member data never more than an hour behind.
High traffic or multisite. Streaming database backups, hourly full, tighter RTO, monthly drills and on-call response inside business hours.
Regulated or mission critical. Immutable retention, audit trail, 24 by 7 on-call response and quarterly business continuity review.
We do not close a backup ticket on a green dashboard. Recovery has to hold up against a real restore, real traffic and a real clock.
Every archive lands on storage that is not the production host so a lost server never means a lost site.
Object versioning with lifecycle rules, so a silent corruption a week ago is still recoverable today.
TLS in transit, SSE on storage, customer held keys on Enterprise. No plain archives on shared drives.
Every upload is hashed and checked. A silently truncated archive is flagged before the next schedule runs.
A monthly sandbox restore, with a written report, proves recovery works before you need to rely on it.
Failed jobs page our on-call engineer first. Your team hears from us only when action is needed.
Targets are agreed after the audit and reviewed every quarter. No vague promises, no moving goalposts.
Site down, hacked, database corrupted, every scenario has a written playbook before the first real incident.
Every restore triggers a root cause review and a change to the backup pipeline or runbook where needed.
We are the silent backup and DR team behind agencies that host, maintain or support WordPress sites. Your clients see your runbook, your restore reports and your brand on every artefact. Our name never appears in the dashboard, the email alerts or the incident call.
Runbooks, drill reports and incident post-mortems carry your brand, not ours.
One point of contact across every client. Shared Slack, scheduled reviews, fast replies when sites go down.
Per-site rates, bulk discounts and priority scheduling for agency partners with recurring care work.
We plug into your ticketing, your monitoring, your on-call rotation. No tool switching for your team.
You send host access, plugin list and any regulatory constraints around data storage and retention.
We inventory the site, write the runbook and send you a partner rate quote. Never shown to your client.
You mark up, brand the proposal and present it on your letterhead at your price.
Your client signs off on the retention, RTO and drill schedule with your brand and pays you directly.
Silent setup, monitoring and drills. No vendor credits, no email signatures, no footer links from us.
You review the drill report each month, accept handover and ship it to your client under your agency name.
Yes. Planning, reviews and support can be organised around GMT/BST. We agree response expectations, meeting windows and escalation contacts before the project or care plan starts.
We apply data minimisation, secure handling and privacy-by-design practices to forms, analytics, integrations and hosting decisions. We document the technical choices clearly, while your legal or data-protection adviser confirms the obligations that apply to your organisation.
Depends on tier and site. A brochure site on daily backups is a four hour RTO and 24 hour RPO. A WooCommerce store on streaming database backups is typically a one hour RTO and under 15 minute RPO. We commit to numbers in writing after the audit.
We default to Backblaze B2 or AWS S3 in a region you choose. Storage sits under your account, with an IAM user we rotate regularly. Encryption keys are yours. If you cancel, you keep the buckets and the data.
Yes. Every plan includes incident response within the on-call window for that tier. Site down, hacked or database corruption, we work the runbook with your team, restore from the last clean archive and write a post-mortem so the root cause is fixed, not just the symptom.
Recovery from a clean archive is included. A full security hardening project, malware removal across a compromised host and attack surface review sit on our Security Hardening page. After a restore, most teams bundle the two so the door is shut behind the fix.
Share the current host, any regulatory constraints and the downtime you can tolerate. A recovery engineer will respond with an audit outline and a written scope within one business day.